Developer-first API security
Know every API.Find the risk before attackers do.
Discover every endpoint from your code, then test authorization and business logic with real context before attackers find the gap.
7-day free trial · No credit card required
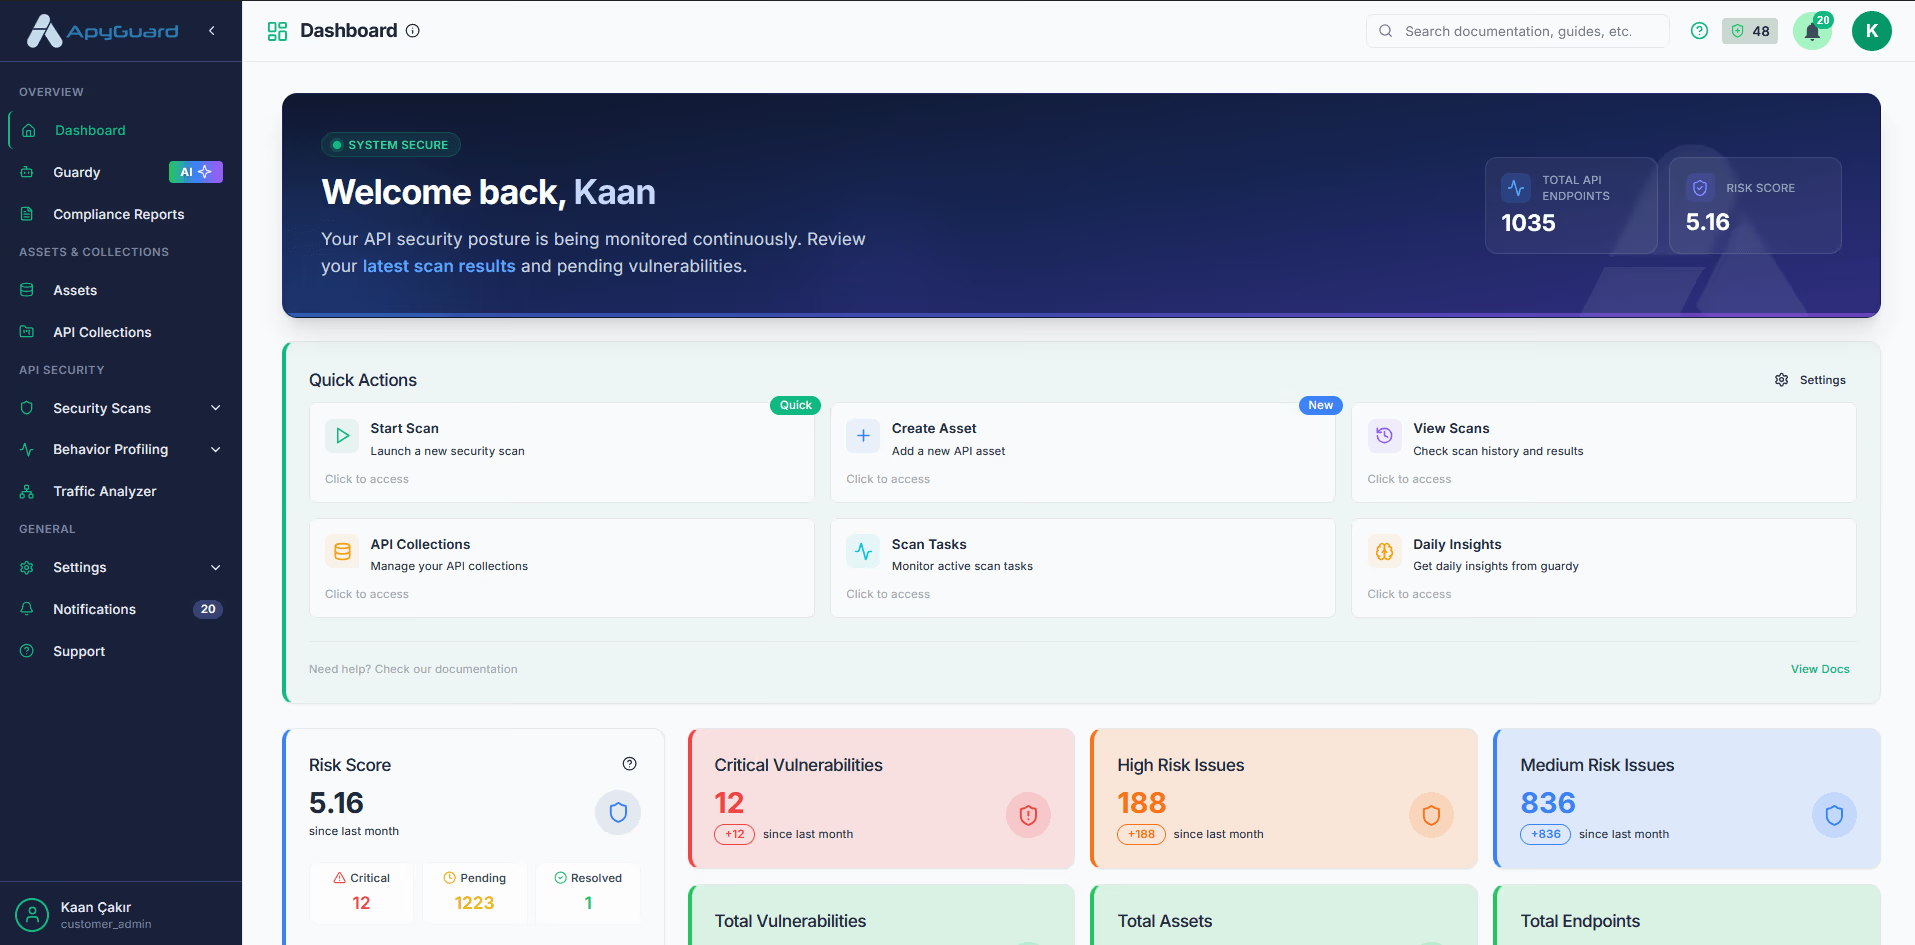
Live security workspace
One view from API surface to reproducible evidence.
Follow authenticated attack paths, behavior signals, and findings without losing the context developers need to fix them.
API security workspace
app.apyguard.com
The visibility gap
Valid requests can still be dangerous.
The hardest API risks use legitimate credentials and technically correct requests. They hide in object access, role boundaries, and business workflows—not syntax.
“A request can pass every schema check and still expose another customer’s data.”
Surface-only scan
- Schema validates
- Status code is 200
- Authentication exists
Result: no issue detected
Context-aware test
- Broken object authorization
- Role and permission drift
- Multi-step workflow abuse
Reproducible evidence
One continuous workflow
From unknown surface to evidence your team can ship.
Security context stays connected from discovery through remediation, so teams spend less time reconstructing what happened.
- 01
Discover
Find the API surface hidden across code, specs, and traffic.
APIScout · OpenAPI · Traffic
- 02
Understand
Map endpoints, schemas, authentication, and role context.
Inventory · Roles · Behavior
- 03
Test
Exercise authorization and business logic with real context.
OWASP · BOLA · Workflows
- 04
Fix & ship
Give engineering teams reproducible evidence and clear guidance.
Evidence · Guidance · CI/CD
See your own API surface in minutes.
7-day free trial · No credit card required
Follow the attack path, not a disconnected alert.
Detailed Visibility Into Your API Security Posture
Our platform provides comprehensive insights into your API security with intelligent analytics and visualizations that help you understand and mitigate risks effectively.
Risk Visualization
Interactive dashboards help you visualize security risks across your API ecosystem and track your security posture over time.
Intelligent Analysis
Pattern recognition maps vulnerability chains across your endpoints, surfacing contextual insights specific to your API architecture and business logic.
Trend Monitoring
Track security trends over time to understand how your security posture is evolving and identify areas for improvement.
API Behavior Profiling
Build behavioral baselines and automatically detect deviations that could indicate security threats, performance issues, or misuse through machine learning.
Security Dashboard
RISK SUMMARY
VULNERABILITY TREND
TOP VULNERABILITIES
Seamless Integrations
ApyGuard integrates with your existing tools and platforms to deliver security throughout the development lifecycle.
GitHub
CI/CD
GitLab
CI/CD
Jenkins
CI/CD
Jira
Workflow
Slack
Notifications
And many more integrations available through our API and webhooks
Why Choose ApyGuard?
Combine schema-aware testing, behavior profiling, and AI-assisted analysis in a workflow developers and security teams can review together.
Automated vs Manual — Why It Matters
- CI/CD-integrated and scheduled scans
- Repeatable testing before release
- OWASP API Security Top 10 coverage
- One platform for scanning, reporting, and monitoring
- One-off engagements, gaps between tests
- Slow turnaround; issues found late
- Coverage depends on consultant and time
- No continuous visibility after the report
Context-Aware Detection: Generate tests from each API's schema and observed behavior instead of relying only on generic signatures.
Reviewable Findings: Requests, responses, and remediation context help teams verify findings before acting.
CI/CD Integration: Bring API security scans into the release workflow.
Behavior Profiling: Add observed API behavior to schema-aware security analysis.
Advanced Reporting: Generate comprehensive reports with actionable insights in just one click.
Team Collaboration: Built-in tools for security teams to collaborate on vulnerability management.
Standards Mapping: Organize findings around OWASP API Security Top 10 categories.
Developers already use APIScout
- APIScout downloads on Open VSX
- 1,596
Security and deployment
Know where each workflow runs
APIScout analyzes supported backend source locally inside VS Code and does not need to execute the application. ApyGuard scanning uses the API target and authentication context you configure. On-premise deployment is available for teams that need testing inside their environment.
Local source discovery
Configured scan targets
Authenticated testing
On-premise option
For legal details, review the Privacy Policy. For deployment requirements, contact the ApyGuard team.
Get Your First Report in Minutes
Discover your API surface and test it for security vulnerabilities before production.
7-day free trial · No credit card required